Decoupling AI Governance from Evidence Retrieval
Enterprise architects must distinguish between audit-ready evidence and the strategic authority required to manage automated decision-making at scale.
Enterprise marketing teams increasingly rely on automated systems like the Salesforce Marketing Cloud or Adobe Experience Platform for bid management and lifecycle orchestration, yet these deployments often outpace the governance frameworks required to manage their outputs. According to a report by MarTech, while observability tools now provide comprehensive audit trails—capturing model versions, input data, and tool calls—this evidence layer only confirms the occurrence of a decision without validating its strategic or operational correctness.
A Decision Receipt serves as the primary artifact for post-incident analysis, documenting the state of the system at the moment of execution. This evidence layer, often integrated into architectures like the Brand Experience AI Operating System (BXAI-OS), allows architects to isolate the specific point of failure within a complex, multi-layered stack. By aligning with the NIST AI Risk Management Framework, organizations can map these receipts into a broader cybersecurity control environment to ensure that every automated action is traceable.
Implementation bugs represent the most common category of failure, where the system configuration fails to adhere to established business rules. In these instances, the authority model remains sound, but the enforcement layer suffers from propagation delays, stale permissions, or logic errors. Engineering teams typically resolve these issues through standard debugging cycles, as the discrepancy between the intended rule and the system output is measurable and clear.
Architectural failures occur when the system functions exactly as configured, yet produces a result that undermines business objectives. When a personalization engine correctly executes a discount rule that ultimately erodes conversion margins, the fault lies in the underlying strategy rather than the code. These scenarios require a revision of the decision architecture, as the system is performing its task with high fidelity to a flawed set of constraints.
Conflict resolution failures arise when multiple, legitimate business rules collide without an established hierarchy of authority. Marketing, finance, and revenue departments may each impose valid constraints on a single offer, leaving the system to rely on vendor defaults or arbitrary configuration settings to resolve the contradiction. These incidents highlight the absence of a centralized authority capable of settling competing business requirements before they reach the deployment phase.
Data drift and context-awareness errors further complicate the governance landscape for enterprise architects. When a system optimizes for a specific metric, such as click-through rate, it may inadvertently violate secondary constraints that were not explicitly encoded into the model’s objective function. Architects must implement validation gates that check for these cross-departmental impacts before the system commits to an action.
The most significant risk to enterprise stability involves the delegation of judgment to systems lacking a defined scope of authority. When a content engine generates promises that the company cannot fulfill—such as offering support services that have been discontinued—the error is not a technical malfunction but an unmade business decision. Systems are frequently tasked with optimizing for engagement metrics without being provided the necessary boundaries to protect corporate reputation or operational reality.
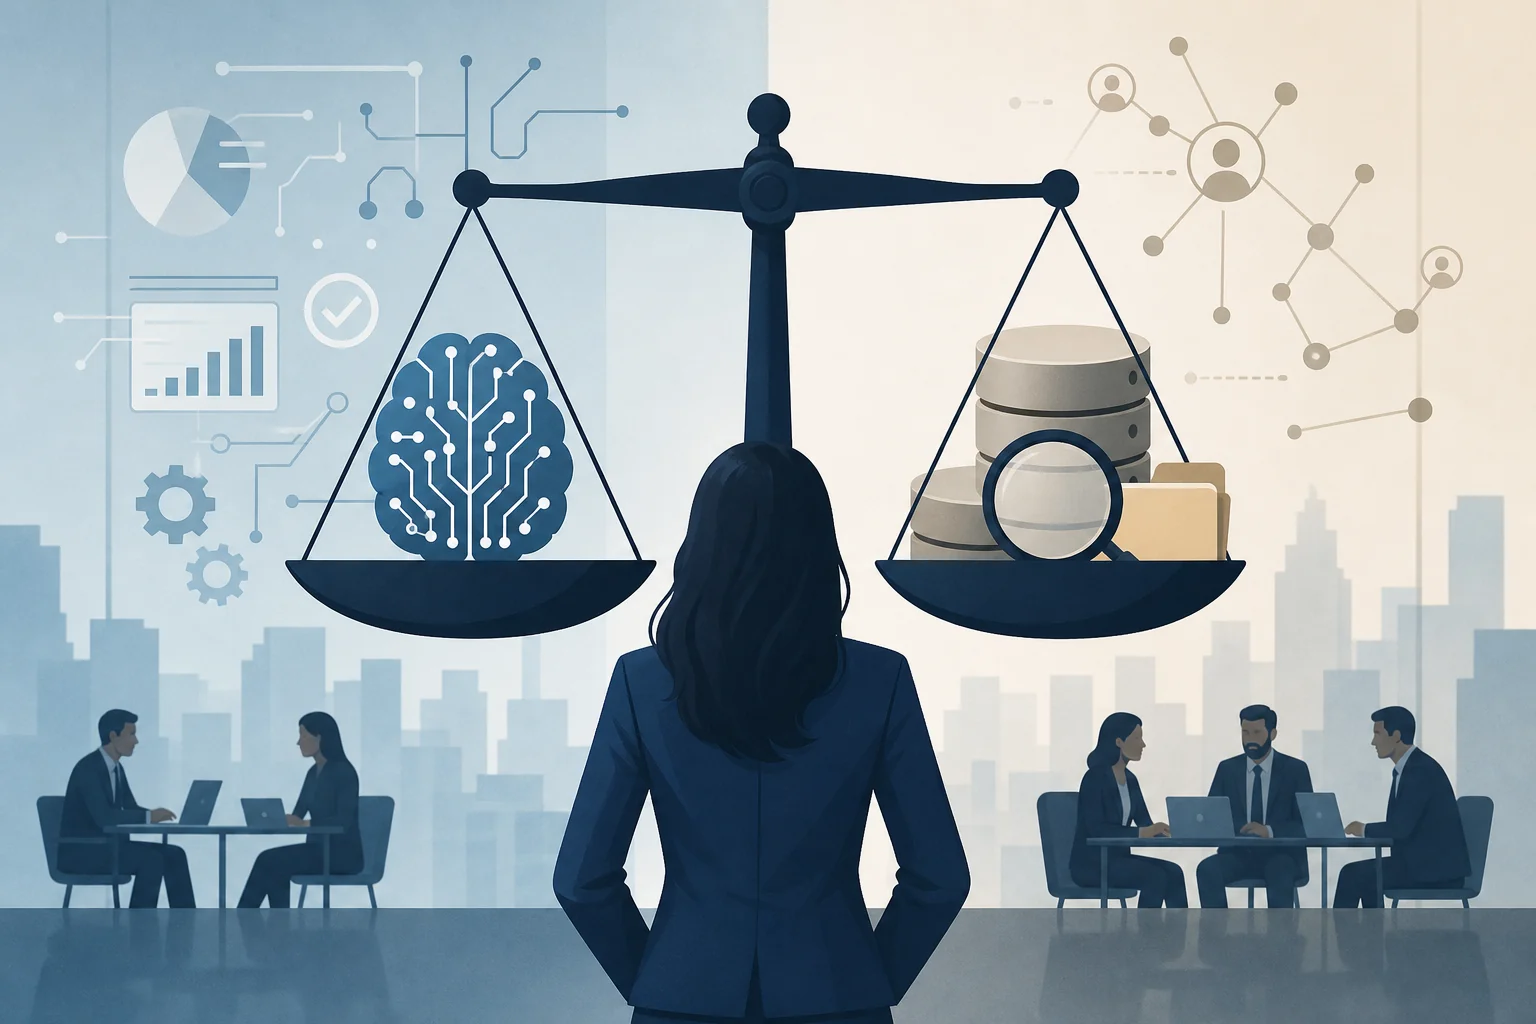
Governance frameworks must distinguish between the technical ability to reconstruct events and the strategic necessity of defining system boundaries. Retrieval-based evidence is a prerequisite for diagnosis, but it does not substitute for the upstream work of resolving conflicting requirements across disparate departments. Architects must ensure that the correction loop includes a human-in-the-loop process to update the governing logic, rather than merely patching the enforcement layer.
Effective governance requires a clear taxonomy that separates upstream policy, runtime enforcement, and downstream evidence. By formalizing this architecture, organizations can move beyond reactive debugging and toward a proactive state of control. Leaders should prioritize the formalization of decision-making hierarchies to prevent automated systems from operating in a vacuum of authority.
Monitoring the frequency of recurring exceptions will reveal whether the failure is a transient implementation error or a systemic conflict in business logic. Future audits should focus on verifying that every automated action is backed by a clear, authorized rule, ensuring that the system is not merely executing instructions but operating within a defined strategic framework.
TAGGED
REFERENCED
RELATED INTELLIGENCE
- MARTECH
Trellist Integrates Automated Qualitative Analysis into Behavioral Data Pipelines
The new Behavioral-to-Qualitative Bridge service automates user interviews to provide diagnostic context for quantitative marketing data.
- MARTECH
Optimizing Retail Innovation Through High-Throughput Concept Evaluation
Retail organizations must transition from resource-intensive validation to rapid, empirical pre-screening to overcome systemic innovation bottlenecks.
- MARTECH
Architecting Career Resilience Against Martech Platform Volatility
Marketing professionals must move beyond vendor-specific tool mastery to survive the rapid consolidation of enterprise platforms and the rise of automated AI agents.