Dymium Introduces GhostAI Gateway for Enterprise Model Governance
Dymium has launched a centralized security gateway designed to enforce governance policies across enterprise AI models and data flows.
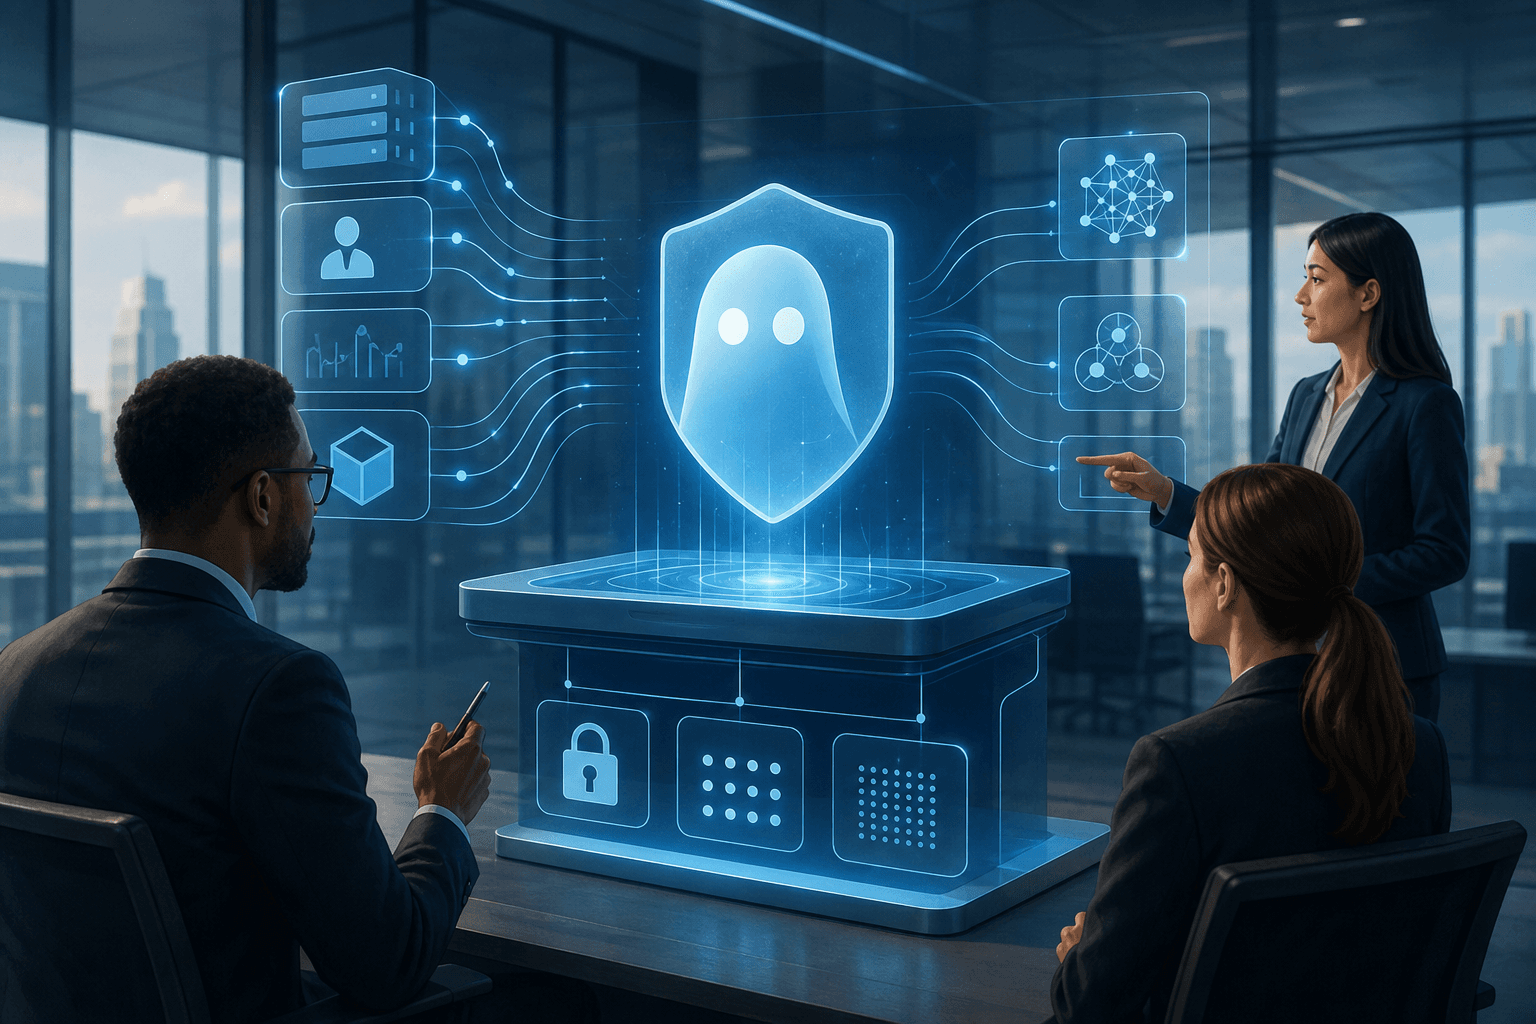
Dymium Inc. has released GhostAI, a security gateway designed to mediate interactions between enterprise data environments and artificial intelligence models. The platform functions as a policy enforcement point, sitting between internal data repositories and external AI agents to inspect, govern, and audit every request in real time.
Denzil Wessels, founder and chief executive officer of Dymium, identified the primary technical conflict as the tension between leveraging proprietary data for model accuracy and maintaining strict privacy compliance. The gateway architecture is segmented into four distinct layers: models, context, tools, and data, which the company claims allows for unified governance rather than fragmented security tooling. By centralizing these controls, the system aims to provide security teams with oversight without forcing employees to abandon their preferred AI workflows.
The model layer within GhostAI supports routing across more than 800 public and private models, enabling administrators to dictate model selection based on data sensitivity and task requirements. Requests involving confidential information can be automatically routed to private inference environments hosted on Amazon Web Services Bedrock, Google Vertex AI, or on-premises data centers. This dynamic routing capability ensures that sensitive workloads remain within authorized infrastructure boundaries.
Data protection is managed through a redaction and masking engine that identifies sensitive information such as credentials, account numbers, and proprietary identifiers before transmission to a model. Dymium employs a zero-copy architecture, which allows AI systems to process live enterprise data without requiring replication or staging in external storage. The system replaces sensitive values with synthetic data during processing and restores original values from a protected vault only after the model returns a response, effectively minimizing the attack surface by ensuring raw data never leaves the secure perimeter.
The context layer utilizes a shared-memory system to manage how organizational knowledge is distributed among users, agents, and models, with policies restricting access based on group or individual permissions. The tools layer integrates with the Model Context Protocol to govern application programming interface calls and external software interactions. By logging every operation, the platform provides an audit trail necessary for organizations operating in highly regulated sectors like financial services and healthcare, ensuring that every interaction is traceable and compliant with internal mandates.
Dymium stated in a recent announcement that early-access customers have been utilizing the underlying technology for approximately six months to secure chat interfaces and agentic workflows. The configuration process is designed for rapid deployment, with the company claiming most organizations can operationalize the gateway in under five minutes. Pricing for the service is structured around consumption metrics rather than flat licensing fees, providing a scalable model for growing enterprise deployments.
The shift toward centralized AI gateways reflects an architectural trend where enterprises are moving away from ad-hoc model adoption toward managed, policy-driven infrastructure. By abstracting security from the underlying model, Dymium allows organizations to swap or upgrade AI providers without rewriting their entire governance framework. This approach reduces the risk of vendor lock-in while maintaining a consistent security posture across diverse AI deployments, which is a critical requirement for modern enterprise stacks.
Technical leaders should evaluate how this gateway interacts with existing identity and access management systems to ensure consistent policy enforcement. The reliance on synthetic data replacement also warrants scrutiny regarding potential latency impacts on complex inference tasks, as the overhead of vault retrieval must be balanced against the necessity of data obfuscation. Monitoring the performance of the Model Context Protocol integration will be essential for teams looking to scale agentic workflows, as this protocol acts as the primary bridge between disparate software tools and the AI models themselves.
Future adoption will likely depend on the platform’s ability to maintain compatibility with the rapidly shifting landscape of open-source and proprietary model APIs. Enterprise architects should watch for the official general availability timeline and assess the long-term total cost of ownership compared to building custom middleware solutions. As the ecosystem matures, the ability to enforce granular, context-aware policies will become the standard for any organization deploying AI at scale.
TAGGED
REFERENCED
- Google Vertex AIcloud.google.com
- Model Context Protocolanthropic.com
RELATED INTELLIGENCE
- AI
Pegasystems Q3 2026 earnings reveal enterprise AI deployment friction
The software provider faces extended sales cycles and operational hurdles as enterprise clients struggle to integrate complex AI workflows into existing architectures.
- AI
Enterprise AI Adoption Faces Operational Friction from Variable Cost Spikes
Enterprises struggle to maintain fiscal control as autonomous agent deployments outpace existing monitoring capabilities and budget governance.
- AI
Establishing Unit Economics for Enterprise AI Workflows
Enterprise leaders must shift from tracking aggregate AI spend to measuring cost-to-outcome ratios to ensure infrastructure investments deliver tangible business value.