Logic Flaw in Burp Suite JWT Editor Extension Exposes HMAC Key Handling
A deep-dive investigation into silent cryptographic failures reveals how automated security tooling can introduce hidden variables during token manipulation.
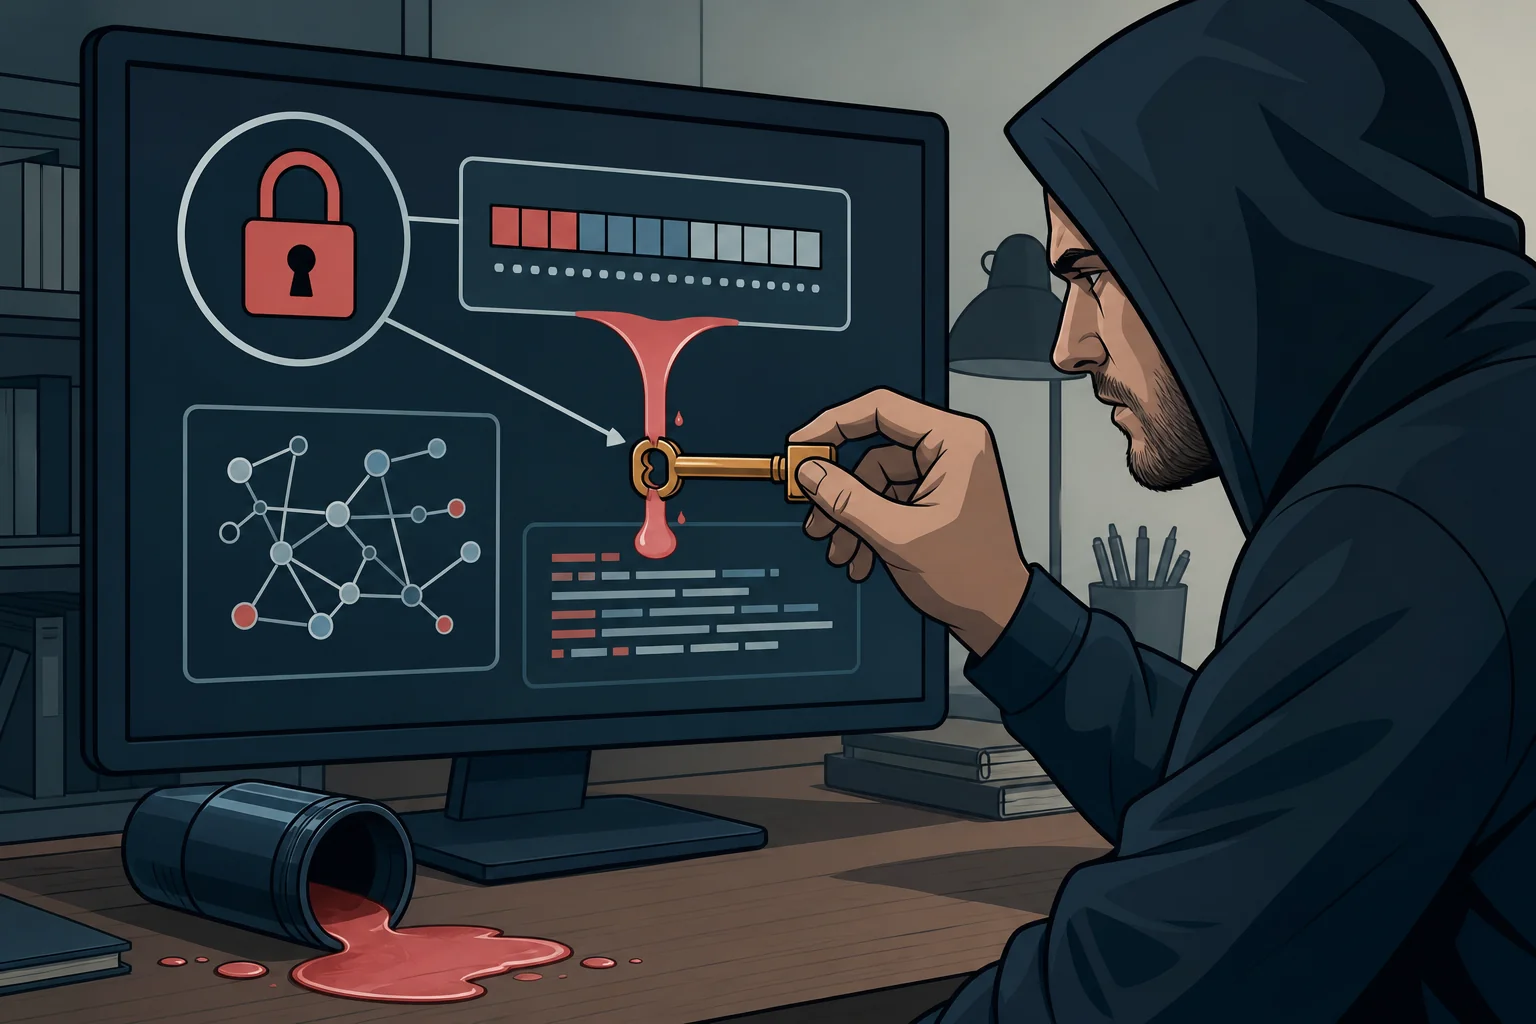
A critical logic flaw within the widely used JWT Editor extension for Burp Suite has been identified, revealing how silent data handling errors can undermine authentication bypass testing. The issue, documented in a technical analysis on HackerNoon, demonstrates that even industry-standard security tooling can inadvertently introduce variables that derail cryptographic verification processes.
The investigation began when a standard JWT algorithm confusion lab, as outlined in PortSwigger Web Security Academy documentation, consistently failed despite the researcher following established protocols. Algorithm confusion occurs when backend systems mistakenly treat a public key as an HMAC secret, allowing attackers to sign tokens using symmetric algorithms like HS256 instead of the expected RS256. This vulnerability relies on the precise formatting of the public key material provided to the verification library.
The researcher spent nearly an hour attempting to solve the lab before questioning the integrity of the tool itself. The researcher verified the steps against community-provided solutions, confirming the methodology was correct. This discrepancy suggested the failure resided within the tooling rather than the user’s implementation, prompting a systematic isolation of variables.
A fresh instance of the lab was deployed to rule out transient state issues, yet the failure persisted. The researcher then utilized an independent tool, rsa_sign2n, to derive key material from two signed tokens, which successfully bypassed the authentication check. This confirmed that the lab environment was functioning as intended, but the manual key entry process within the JWT Editor extension was producing a different result.
Comparing the Base64-encoded strings side-by-side revealed no obvious differences, as both strings appeared identical in their PEM-encoded format. The researcher turned to Burp Comparer to conduct a byte-level analysis of the raw data. By switching to a hexadecimal view, the investigation uncovered a hidden, non-obvious difference in the data structure that the extension was introducing during the key import process.
The hexadecimal analysis revealed that the extension was appending or modifying specific non-printable control characters during the parsing of the PEM block. These subtle byte-level alterations, while invisible to standard text editors or terminal displays, fundamentally changed the cryptographic signature of the key. Because the backend verification library required an exact bit-for-bit match to validate the HMAC secret, these invisible modifications caused the signature to fail every time.
This silent contamination of the HMAC key highlights a significant risk in security testing, where tools may subtly alter input data without alerting the user. When an extension handles cryptographic keys, any deviation from the expected format—even if invisible in standard text editors—can lead to failed signatures and invalid test results. Such logic flaws demonstrate the necessity of validating tool output against independent, low-level scripts when complex cryptographic operations are involved.
For enterprise security teams and penetration testers, this incident serves as a reminder that automated tooling is not infallible. Relying exclusively on high-level extensions for sensitive operations like token manipulation can mask underlying technical failures. Architects should prioritize the use of verified, transparent scripts for cryptographic tasks to ensure that the security posture of an application is being tested against the actual implementation rather than a tool’s internal interpretation.
The discovery underscores the importance of maintaining a modular and verifiable security stack. When automated extensions fail to produce expected results, practitioners must be prepared to drop down to the protocol layer to inspect raw data. Future testing cycles should incorporate cross-verification steps to ensure that tool-specific logic does not introduce false negatives in vulnerability assessments.
Security leaders should monitor for similar discrepancies in automated workflows where cryptographic keys are managed by third-party plugins. By establishing a baseline of manual verification for critical authentication tests, teams can mitigate the risk of silent failures. The next milestone for practitioners involves auditing the import logic of common extensions to identify if similar contamination risks exist in other cryptographic modules.
TAGGED
REFERENCED
- PortSwigger Web Security Academy documentationportswigger.net
- independent tool, rsa_sign2ngithub.com
RELATED INTELLIGENCE
- INFRASTRUCTURE
BSEC Proposes Unified Back-Office Architecture to Mitigate Brokerage Fraud
The Bangladesh Securities and Exchange Commission is evaluating a centralized software framework to standardize brokerage monitoring and prevent asset misappropriation.
- AI
Pegasystems Q3 2026 earnings reveal enterprise AI deployment friction
The software provider faces extended sales cycles and operational hurdles as enterprise clients struggle to integrate complex AI workflows into existing architectures.
- AI
Enterprise AI Adoption Faces Operational Friction from Variable Cost Spikes
Enterprises struggle to maintain fiscal control as autonomous agent deployments outpace existing monitoring capabilities and budget governance.