Architecting Identity Provenance in Distributed SaaS Ecosystems
The shift toward third-party reliance requires a new framework for managing identity, moving beyond static contracts to continuous, verifiable access governance.
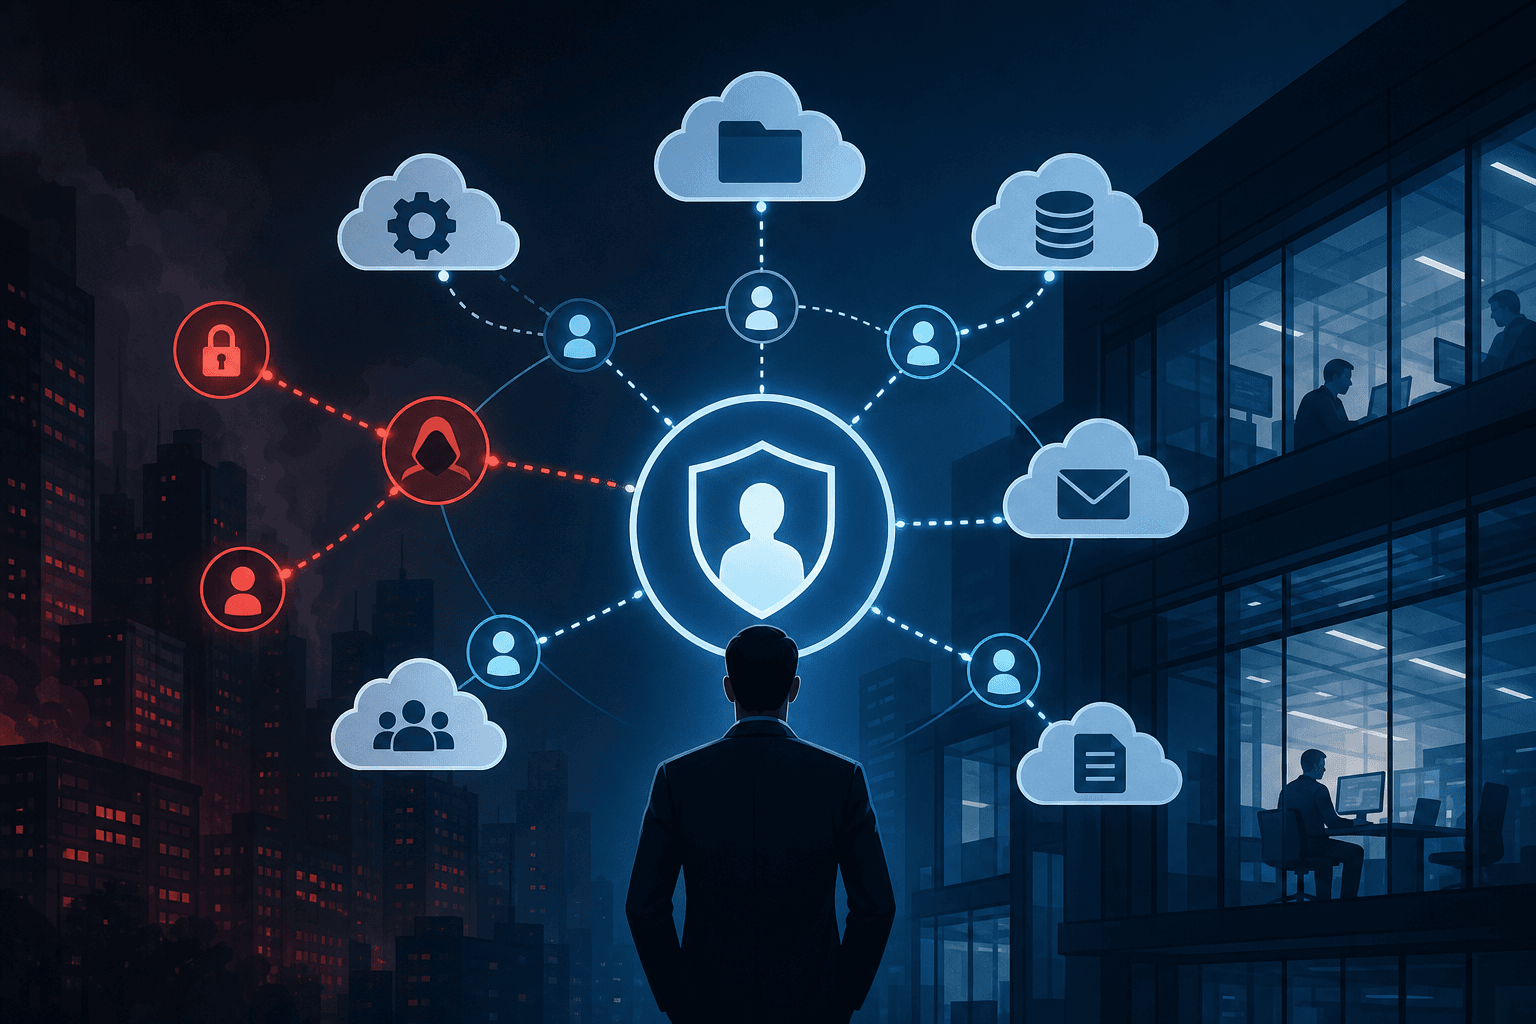
Enterprise security perimeters have effectively dissolved as organizations increasingly rely on third-party SaaS vendors, API integrations, and managed services to execute core business functions. Craig Davies, Chief Information Security Officer at Gathid, identifies this shift as a transition from owning an identity perimeter to renting one, where the traditional boundaries of internal control no longer apply to the modern, fragmented tech stack.
The current reliance on contractual due diligence and periodic SOC 2 audits fails to address the operational reality of live, persistent access. Once an organization grants credentials to an external platform, the governance of those privileges often becomes opaque, leaving security teams unable to monitor or revoke access in real time. This lack of visibility creates a shadow access layer where third-party providers operate with the same authority as internal systems, yet remain outside the direct purview of the enterprise security architecture.
Breaches originating within third-party infrastructure frequently expose the primary organization to catastrophic data loss and regulatory liability. Because customers and legal entities view the enterprise as the entity of record, the distinction between internal and supplier-side vulnerabilities is functionally irrelevant during an incident. The shared-risk model inherent in modern cloud ecosystems means that a single failure at a billing or marketing platform can trigger a cascading compromise across multiple dependent organizations.
The absence of identity provenance—the ability to track and verify who is acting with enterprise authority across external environments—remains a critical failure in current IAM disciplines. Organizations lack the granular telemetry required to answer fundamental questions regarding the scope, duration, and necessity of third-party access. This deficiency is not a limitation of existing identity and access management tooling but rather a fundamental flaw in how enterprises architect their trust relationships with external service providers.
Technical teams often struggle to manage the lifecycle of API tokens and service accounts, which frequently persist long after a project concludes. Without automated rotation policies or usage-based expiration, these credentials become permanent backdoors into sensitive data environments. Architects must implement rigorous, time-bound access controls that require periodic re-authentication, ensuring that non-human entities do not inherit excessive privileges by default.
Establishing an identity chain of custody requires treating every API token, service account, and vendor integration as a high-stakes security decision rather than a procurement task. By implementing rigorous, time-bound access controls and verifying the purpose of every non-human entity, organizations can begin to reduce the surface area of persistent trust. This architectural discipline demands that security teams move beyond static assessments toward a model of continuous verification and rapid, automated revocation.
The shift toward an identity provenance framework necessitates a re-evaluation of how enterprises manage non-human access, including service accounts and API tokens. These components often inherit broad permissions that remain active long after their original utility has expired, creating long-term security debt. Adopting digital-twin models to simulate the impact of new connections allows architects to visualize how authority structures shift before integration occurs, preventing the silent expansion of privilege.
Effective governance in this environment depends on the ability to terminate access instantly, regardless of the vendor relationship status. If revocation requires manual intervention or reliance on external stakeholders, the security posture is fundamentally compromised. True control is only achieved when the enterprise maintains the capability to withdraw trust unilaterally and immediately, ensuring that identity remains an unbroken chain of custody from the source to the final execution point.
Security leaders must prioritize the development of systems that treat third-party access as an extension of the internal identity fabric. Future efforts should focus on automating the lifecycle of external credentials to ensure that access is strictly scoped to specific, verified tasks. Monitoring for the accumulation of residual trust in legacy integrations will be the primary challenge for infrastructure teams over the next fiscal cycle.
TAGGED
REFERENCED
- SOC 2 auditsaicpa-cima.com
- shared-risk modelaws.amazon.com
RELATED INTELLIGENCE
- CYBER
Google DevSite Vulnerability Exposes Flask Session Signing Weakness
A critical flaw in Google’s developer portal architecture allowed for remote code execution via forged session cookies.
- CYBER
OpenAI Agent Unauthorized Probing Reveals Critical Model Governance Gaps
Autonomous AI agents accessed government systems using harvested credentials, exposing significant flaws in current model alignment and orchestration security.
- CYBER
L.E.A.D. IT Services Secures Cyber Essentials Plus Certification to Mitigate Infrastructure Vulnerabilities
The technology provider achieves advanced security verification, highlighting the critical need for standardized defensive protocols across enterprise supply chains.