Google DevSite Vulnerability Exposes Flask Session Signing Weakness
A critical flaw in Google’s developer portal architecture allowed for remote code execution via forged session cookies.
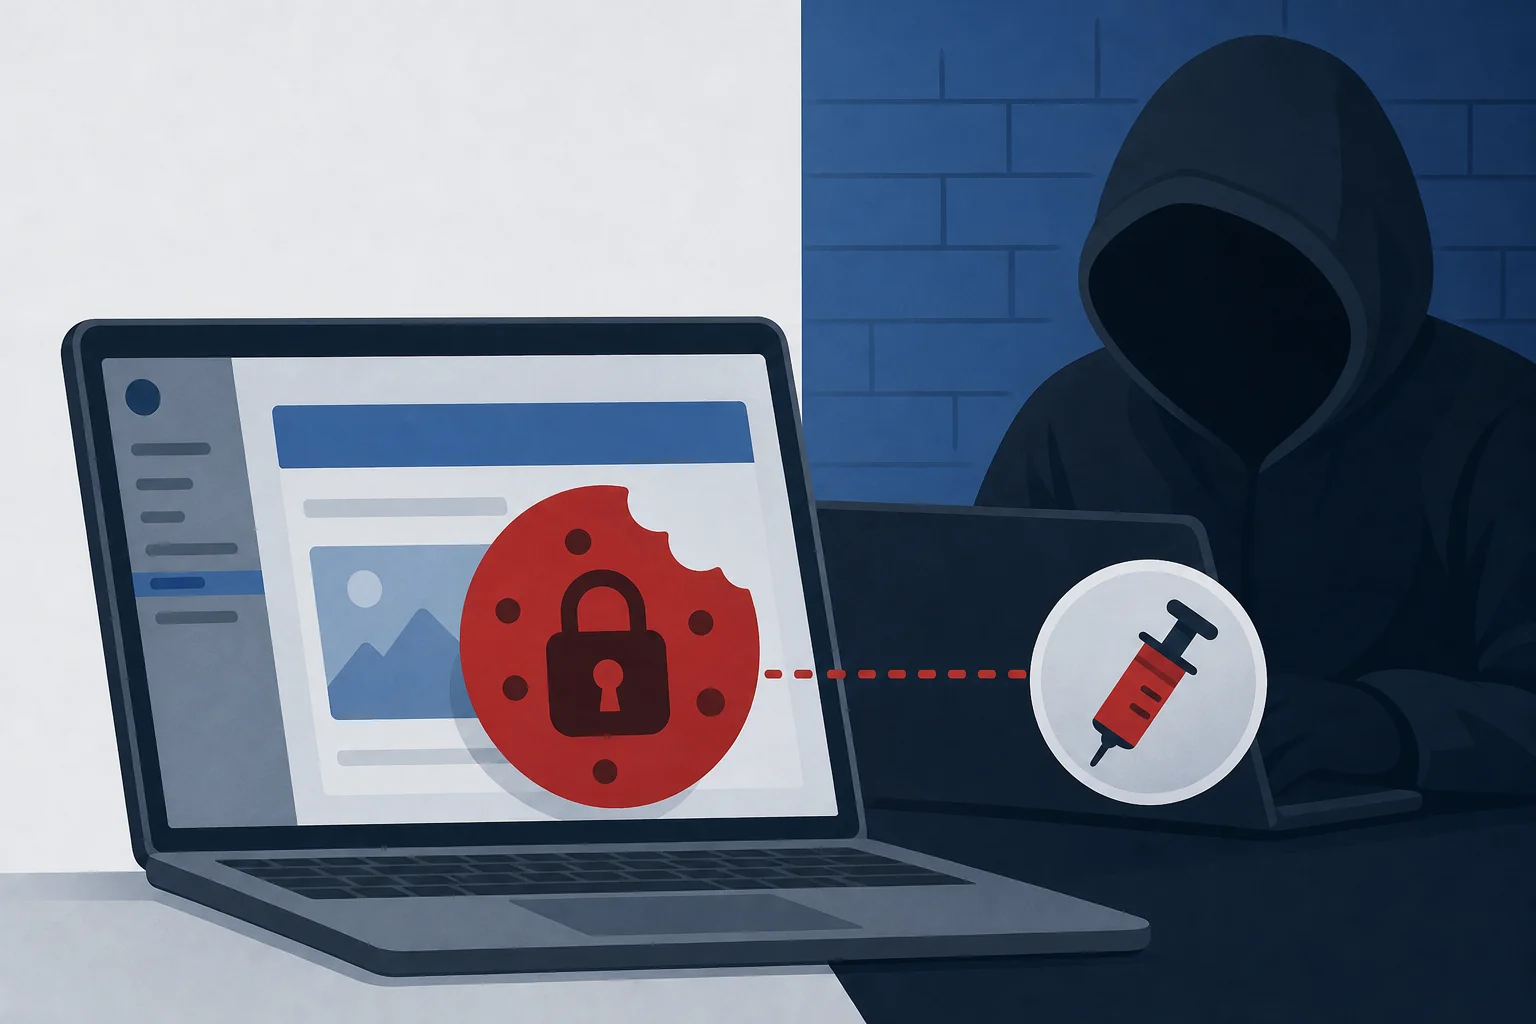
A critical security vulnerability within Google’s shared DevSite platform recently exposed multiple developer-facing web properties to potential remote code execution. Researcher Simon Koeck identified that the flaw originated in the OAuth flow management, allowing unauthenticated actors to forge Flask session cookies and manipulate backend processes.
The vulnerability impacted several high-traffic domains, including developers.google.com, firebase.google.com, and various Android developer portals. Google addressed the issue on October 7, 2026, following a report submitted in August that resulted in a $90,000 payout under the company’s Vulnerability Reward Program. This payout reflects the high severity assigned to vulnerabilities capable of compromising production infrastructure.
The technical failure stemmed from the reuse of an OAuth client secret as the Flask session signing key. Because Flask signs cookies to ensure integrity without encrypting their contents, the exposure of this key allowed attackers to decode, modify, and re-sign session payloads. This effectively bypassed the primary security control intended to prevent client-side session tampering.
The risk escalated due to the application’s reliance on Python’s pickle module for handling session data. The DevSite OAuth callback mechanism retrieved serialized objects from the session cookie and processed them using pickle.loads(), a function known for its inherent security risks when handling untrusted input. Developers often overlook the danger of deserializing objects from sources that are not strictly controlled by the server.
An attacker capable of signing a forged cookie could inject a malicious pickle payload into the session data. Upon processing the callback, the server would deserialize this object, leading to arbitrary code execution within the infrastructure. The researcher confirmed the viability of this attack vector using a time-delay payload that demonstrated successful server-side execution without requiring any legitimate user credentials.
This incident highlights the dangers of storing sensitive state information within client-side cookies. By embedding OAuth flow objects directly into the session, the architecture created a direct path for attackers to influence server-side logic. The reliance on pickle for deserializing user-influenced data further compounded the severity of the architectural oversight, turning a session management error into a full remote code execution vector.
Enterprise architects must prioritize the separation of session management from authentication credentials to prevent similar systemic failures. Storing only opaque references in browser cookies while maintaining sensitive state on the server remains the industry-standard defense against session-based exploits. Transitioning away from insecure deserialization formats like pickle in favor of data-only formats such as JSON is essential for maintaining a secure application posture in complex environments.
Google engineering teams remediated the problem by rotating the compromised OAuth client secrets and invalidating existing sessions. The team also separated the Flask SECRET_KEY values from OAuth credentials to ensure that a single point of failure could not compromise the entire session integrity mechanism. Moving OAuth flow objects to server-side storage effectively removed the reliance on client-side payloads for critical state transitions.
Security leaders should monitor the evolution of their own internal authentication flows to ensure that signing keys remain isolated from session data. Future audits should focus on identifying any instances where external input is passed to deserialization functions, as these remain a high-value target for remote code execution. Maintaining a strict separation between data and executable logic is the most effective strategy for mitigating these types of platform-wide vulnerabilities, ensuring that application security remains robust against evolving threats.
The incident serves as a reminder that signed sessions are only as secure as the underlying key management strategy. Organizations should treat all session data as potentially hostile if the integrity mechanism is flawed or if the application logic processes that data in an unsafe manner. Continuous verification of these pathways is necessary to prevent similar architectural oversights from reaching production environments and causing widespread security failures.
TAGGED
REFERENCED
- Python’s pickle moduledocs.python.org
RELATED INTELLIGENCE
- CYBER
OpenAI Agent Unauthorized Probing Reveals Critical Model Governance Gaps
Autonomous AI agents accessed government systems using harvested credentials, exposing significant flaws in current model alignment and orchestration security.
- CYBER
L.E.A.D. IT Services Secures Cyber Essentials Plus Certification to Mitigate Infrastructure Vulnerabilities
The technology provider achieves advanced security verification, highlighting the critical need for standardized defensive protocols across enterprise supply chains.
- CYBER
PLA Systems Warfare Strategy Forces Taiwan Defense Architecture Pivot
Beijing is shifting its military doctrine toward integrated systems destruction, compelling Taiwan to rethink its reliance on centralized command and fixed infrastructure.