Architectural Shifts in Sovereign AI Deployment
Enterprises are moving beyond public cloud reliance to secure AI workloads, necessitating a fundamental redesign of infrastructure, observability, and deployment pipelines.
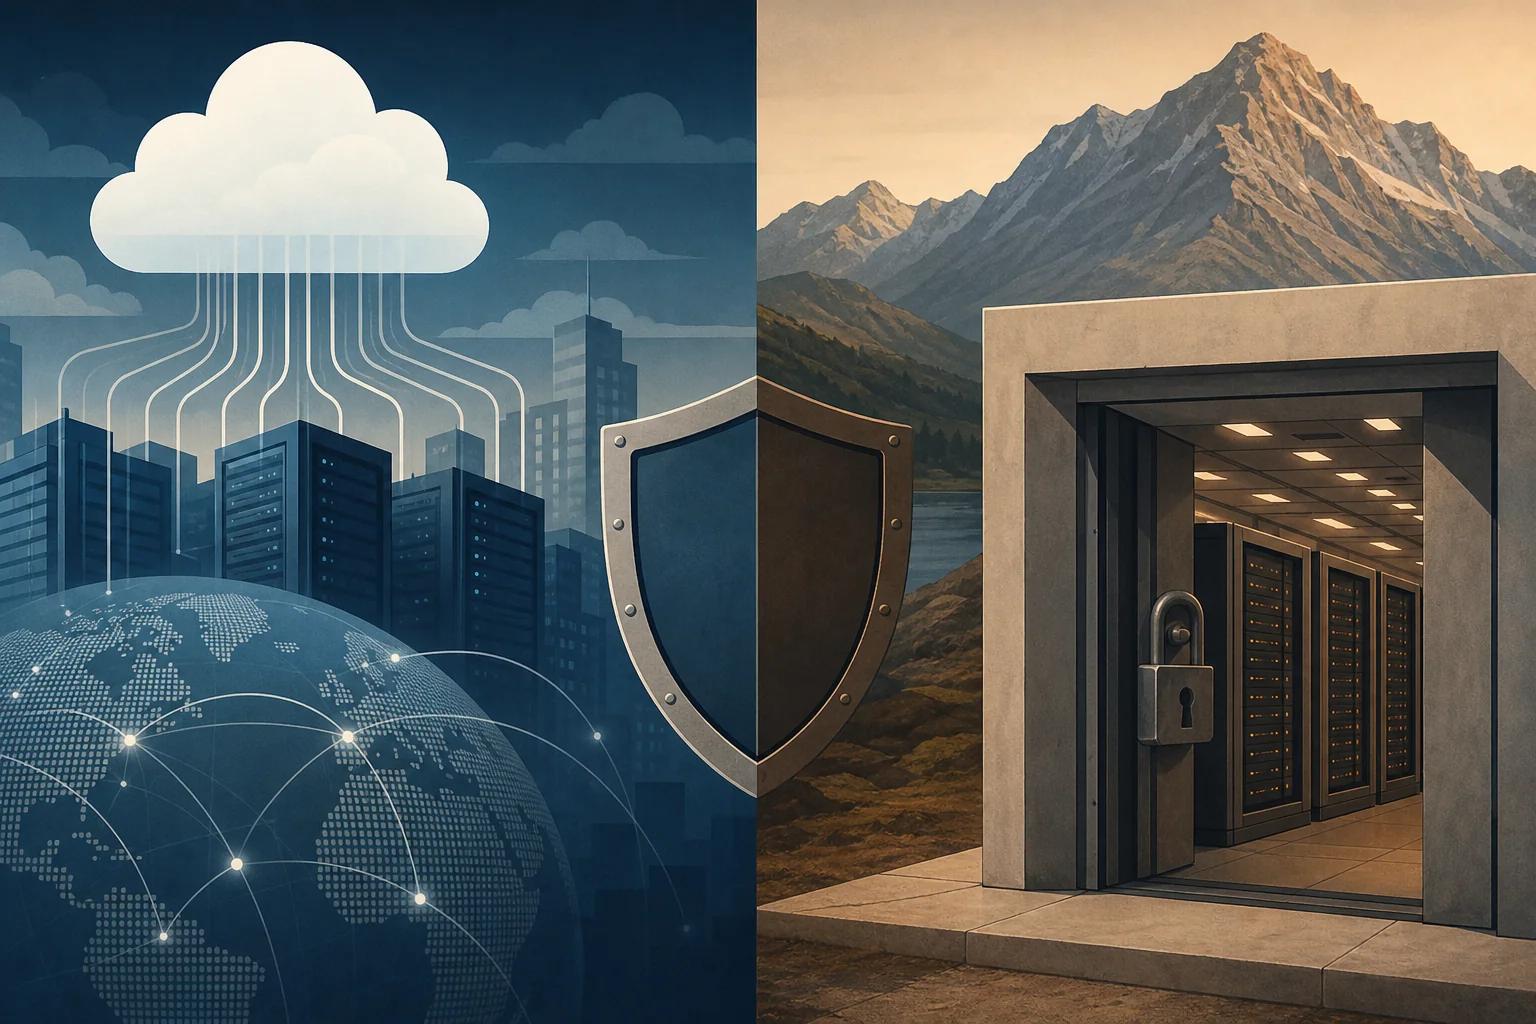
Organizations increasingly find that public cloud environments fail to satisfy the stringent legal, operational, and security requirements necessary for sensitive artificial intelligence workloads. Karan Alang, a principal software engineer at Versa Networks, notes in a recent report that while cloud platforms offer initial agility, they often lack the granular control over data residency and infrastructure access required for sovereign AI.
Data sovereignty extends beyond simple geographic storage, encompassing the control of personnel, system operations, and access paths. In the context of AI, this complexity multiplies as data flows through training pipelines, vector databases, and inference systems. Autonomous agents further complicate the security posture by acting on data in ways that traditional, static database controls cannot easily govern.
Sovereign cloud environments offer a middle ground, providing regional constraints and managed controls while still relying on provider-owned infrastructure. This model allows for some degree of jurisdictional compliance, yet customers remain tethered to the provider’s hardware roadmap, API ecosystem, and service availability. For many enterprises, this dependency on a third-party service roadmap presents an unacceptable risk to long-term operational autonomy.
Air-gapped environments provide the highest level of control by isolating data and compute within an organization-managed facility. Historically, the high cost and management burden of these deployments rendered them impractical for most AI initiatives. Recent advancements in local large language model inference and the maturation of open-source infrastructure stacks have fundamentally altered this economic calculus.
Enterprise-grade servers equipped with modern GPUs now support significant inference workloads outside of hyperscale data centers. Techniques such as model quantization allow organizations to run sophisticated models on internal hardware without relying on external APIs. This shift enables teams to bring cloud-native principles, such as those found in Kubernetes or Apache Spark, into air-gapped environments without sacrificing performance.
Transitioning to an air-gapped sovereign AI architecture requires a departure from the elastic assumptions of public cloud computing. Capacity is finite, necessitating precise upfront sizing for CPU, memory, and GPU allocation to handle peak loads. Engineering teams must account for the lead time associated with physical hardware procurement, which replaces the instant provisioning capabilities of cloud providers.
Hardware procurement cycles often introduce significant delays that require architects to forecast demand months in advance. Unlike the cloud, where resources scale horizontally with a few API calls, on-premise sovereign AI requires a rigid commitment to physical inventory. This shift forces organizations to balance the risk of over-provisioning against the potential for performance bottlenecks during periods of high demand.
Observability and management functions that are typically handled by managed cloud services must be rebuilt from the ground up. Organizations must implement internal log aggregation using tools like Grafana and Loki to maintain compliance and system visibility. CI/CD pipelines also require a complete redesign to support internal artifact registries, ensuring that software distribution remains secure and isolated from external networks.
Securing the CI/CD pipeline in an air-gapped environment introduces unique challenges regarding the verification of software provenance. Without access to public repositories, teams must implement rigorous scanning and signing protocols for every container image and model weight file. This internal registry management becomes a critical security layer, preventing the introduction of unauthorized code into the sovereign production environment.
The shift toward sovereign AI demands that architects treat infrastructure control as a first-class design requirement rather than an afterthought. Leaders should prioritize the selection of hardware and models that align with specific operational needs, such as high-volume telemetry processing or language-based investigation. Failure to integrate these considerations into the initial platform design often leads to costly, complex retrofitting efforts that undermine the intended security benefits.
Future enterprise strategy must account for the trade-off between the flexibility of the cloud and the control of sovereign infrastructure. As organizations continue to embed AI into mission-critical workflows, the ability to maintain an air-gapped or highly controlled environment will become a primary differentiator for regulated industries. Monitoring the development of portable, open-source AI stacks will be essential for architects aiming to balance innovation with strict governance requirements.
TAGGED
REFERENCED
- Apache Sparkspark.apache.org
- Grafana and Lokigrafana.com
RELATED INTELLIGENCE
- INFRASTRUCTURE
AWS Scales FSx for Lustre Metadata Throughput for Intensive HPC Workloads
The cloud provider has increased metadata I/O capacity for its Intelligent-Tiering storage class, addressing a common bottleneck for large-scale research and machine learning environments.
- INFRASTRUCTURE
Architectural Deficiencies in CMS Platforms Impacting Search Indexing
Enterprise CMS platforms frequently lack native SEO controls, forcing technical teams into unsustainable manual workarounds and reliance on insecure third-party plugins.
- INFRASTRUCTURE
Microsoft Windows Memory Optimization Targets 8GB RAM Constraints
Microsoft is re-engineering Windows to maintain performance on low-memory hardware as the industry faces persistent supply chain constraints.