CyberNX Deploys NXRadar for Automated SBOM Lifecycle Governance
The new platform automates software bill of materials generation to meet stringent regulatory compliance mandates for financial and critical infrastructure entities.
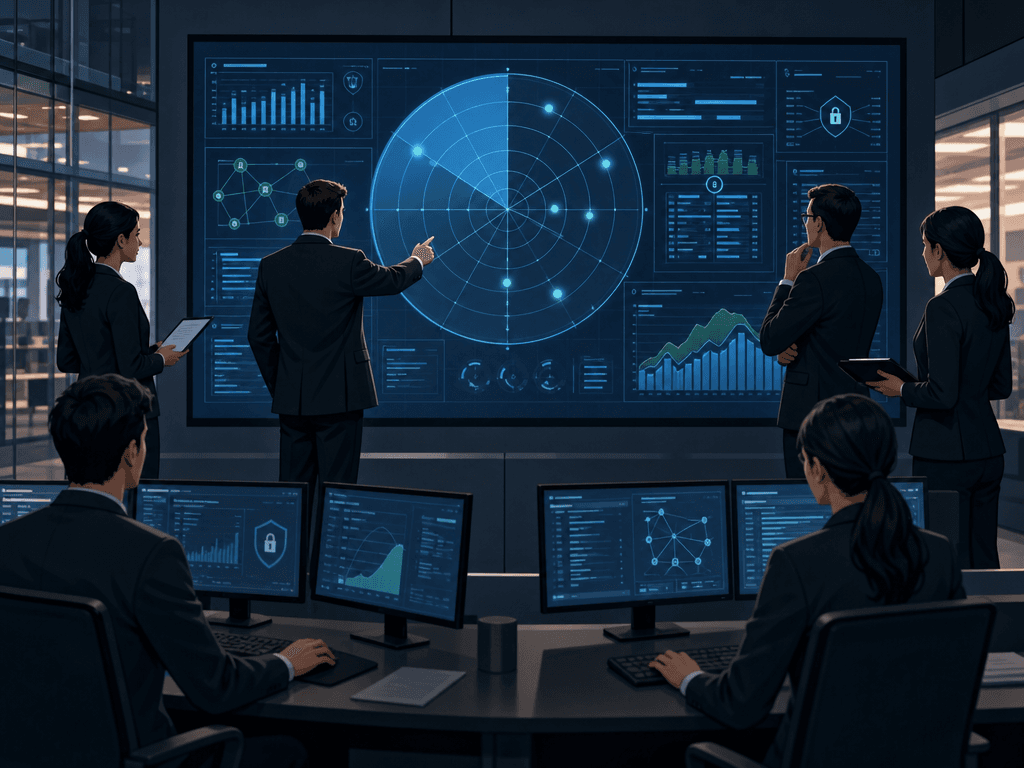
CyberNX has launched NXRadar, an AI-enabled platform designed to automate the generation and governance of software bill of materials (SBOM) for organizations operating within highly regulated sectors.
Modern enterprise applications frequently incorporate thousands of third-party dependencies, creating significant security blind spots that traditional, point-in-time inventory methods fail to capture. NXRadar utilizes a multi-source engine to ingest data from source code repositories, binary files, container images, and CI/CD pipelines to construct a comprehensive view of the software estate.
This automated discovery process replaces manual documentation, which is often prone to human error and latency. By capturing data directly from the build environment, the system ensures that the inventory reflects the actual state of an application rather than a stale snapshot.
The platform employs an auto-regenerating mechanism that updates the SBOM as code changes occur across development environments. This persistent record-keeping is essential for organizations where surveillance audits place emphasis on current evidence.
CyberNX engineered the tool to support entities operating under the mandates of the Reserve Bank of India, the Securities and Exchange Board of India, and the Indian Computer Emergency Response Team. The company stated that these regulatory frameworks require organizations to maintain auditable proof of their software composition.
The platform integrates directly into DevSecOps workflows, allowing security and compliance teams to maintain a continuous, audit-ready record of their software components. It supports industry-standard formats such as SPDX and CycloneDX, facilitating interoperability with existing security tooling and ensuring that documentation meets international reporting standards.
This architectural approach shifts the focus from static compliance checklists to continuous governance of the software supply chain. By embedding SBOM generation into the deployment pipeline, organizations can ensure that every release is accompanied by a verified inventory.
The system provides a unified dashboard that serves as an authoritative record for security teams managing unlimited applications and services. This centralized view reduces the operational overhead associated with tracking dependencies across heterogeneous environments.
The platform correlates SBOM data with live vulnerability feeds to provide risk scoring at the component level. This functionality allows security teams to prioritize remediation efforts based on actual exposure rather than relying on static vulnerability lists.
When new Common Vulnerabilities and Exposures are disclosed, the system identifies affected components across the entire application portfolio to reduce the window of exposure. This capability is particularly critical for regulated sectors where the time between vulnerability disclosure and auditor scrutiny continues to narrow.
By automating the mapping of vulnerabilities to specific software components, the system enables faster response times during security incidents. This risk-based prioritization helps teams allocate resources more effectively to address the most significant threats.
Deployment options include both SaaS and on-premise models to satisfy internal security and data residency constraints. CyberNX stated that the system captures only technical metadata, such as dependency lists and license information, while excluding personal or sensitive data.
This design choice aims to balance the need for granular visibility with organizational data privacy requirements. The platform is designed to install an industry-accepted data-capturing mechanism on the client’s server to process raw component files.
This ensures that sensitive source code remains within the organization’s perimeter while still generating the necessary compliance reports. The flexibility in deployment models allows the platform to fit into diverse infrastructure architectures, from cloud-native environments to legacy on-premise data centers.
Regulated entities face increasing pressure to demonstrate that their security controls are not only implemented but actively maintained. NXRadar provides a dashboard that serves as an authoritative record for auditors seeking evidence of current software composition.
The platform operationalizes the distinction between merely generating an SBOM and maintaining a governed, auditable software inventory. This distinction is vital for organizations that must prove compliance with evolving regulatory frameworks.
By providing a defensible, documented proof of software component governance, the platform helps organizations meet the stringent requirements of their respective regulators. The ability to demonstrate active maintenance of the software supply chain is becoming a prerequisite for maintaining operational licenses in the financial and critical infrastructure sectors.
The shift toward automated SBOM management reflects a broader trend in enterprise security where regulatory scrutiny is moving toward real-time evidence. Organizations must now account for the entire lifecycle of third-party components, from initial integration to end-of-life.
The ability to maintain an accurate, up-to-date inventory is becoming a prerequisite for meeting the evolving expectations of financial and national security regulators. As the software supply chain continues to grow in complexity, the reliance on automated governance tools will likely become standard practice for enterprise architects.
Leaders should evaluate how their current CI/CD pipelines handle dependency tracking and whether existing manual processes can withstand the increasing frequency of regulatory audits. Monitoring the platform’s ability to integrate with diverse build systems will be essential for assessing its long-term utility in complex, heterogeneous enterprise environments.
TAGGED
REFERENCED
- regulatory frameworksassets.kpmg.com
- SPDX and CycloneDXsbomify.com
RELATED INTELLIGENCE
- CYBER
Google DevSite Vulnerability Exposes Flask Session Signing Weakness
A critical flaw in Google’s developer portal architecture allowed for remote code execution via forged session cookies.
- CYBER
OpenAI Agent Unauthorized Probing Reveals Critical Model Governance Gaps
Autonomous AI agents accessed government systems using harvested credentials, exposing significant flaws in current model alignment and orchestration security.
- CYBER
L.E.A.D. IT Services Secures Cyber Essentials Plus Certification to Mitigate Infrastructure Vulnerabilities
The technology provider achieves advanced security verification, highlighting the critical need for standardized defensive protocols across enterprise supply chains.