Mitigating AI Hallucination Risks in Digital Forensic Workflows
Researchers are developing structured validation frameworks to address the critical challenge of AI-generated fabrications in digital forensic investigations.
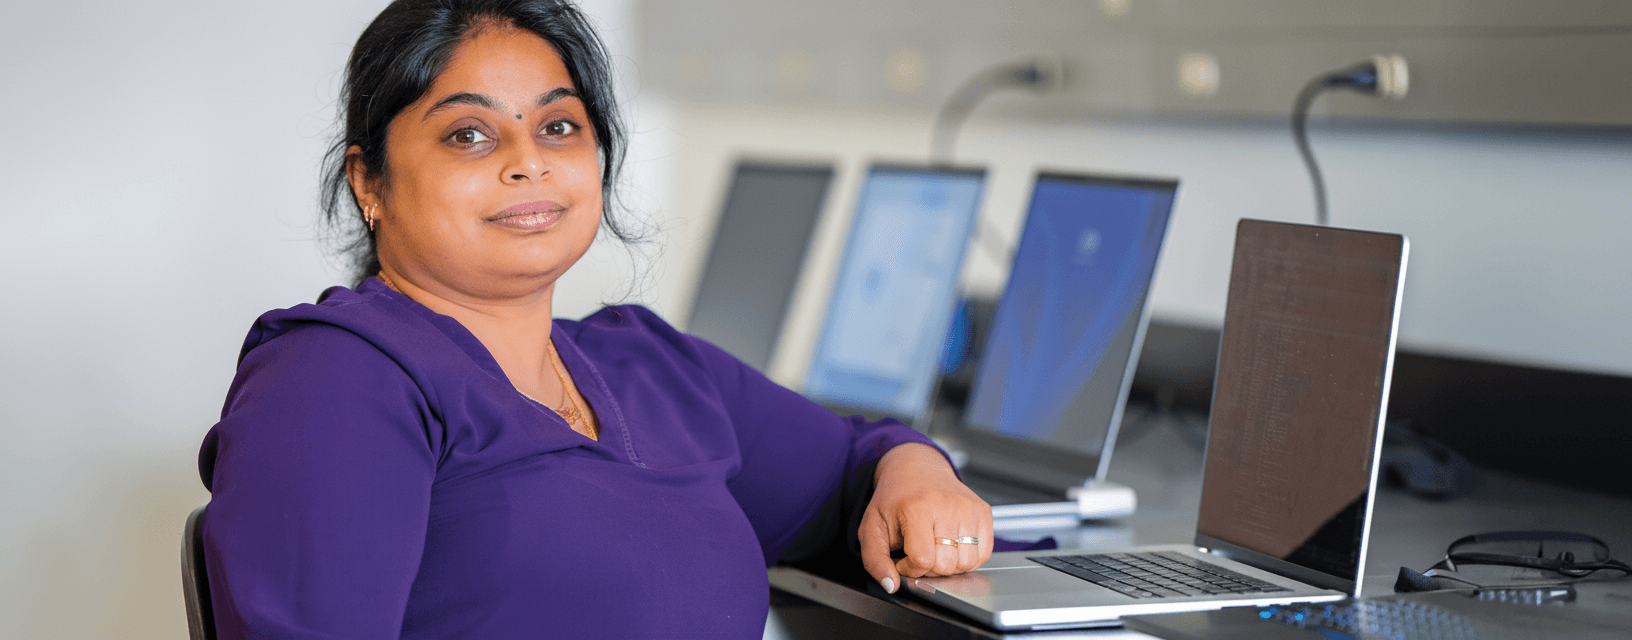
Digital forensic investigations face a significant integrity challenge as generative artificial intelligence models increasingly influence the analysis of system logs, network traces, and memory artifacts. Sneha Sudhakaran, an assistant professor in the Department of Electrical Engineering and Computer Science at Florida Tech, is leading research into the systematic identification and mitigation of AI hallucinations within these high-stakes environments.
The core issue involves the tendency of large language models to generate plausible but technically incorrect or fabricated explanations for complex forensic data. When these models process intricate artifacts, they may produce outputs that appear authoritative yet lack evidentiary support. This phenomenon risks the misinterpretation of digital evidence, which could compromise the validity of investigative conclusions and legal outcomes. Sudhakaran and her team of graduate students are currently mapping the specific scenarios where these models fail to maintain factual accuracy during forensic processing.
Specific failure modes often emerge when models attempt to parse complex system logs or volatile memory structures. For instance, when analyzing Windows Event Logs or Linux syslog files, an AI might misinterpret timestamp correlations or incorrectly attribute specific process IDs to malicious activity. These errors occur because the model prioritizes linguistic coherence over the rigid, syntax-heavy requirements of forensic data structures. The risk is particularly acute in memory analysis, where the model may hallucinate the presence of specific API hooks or memory-resident malware strings that do not exist in the actual memory dump.
Network traces present another layer of complexity where AI models frequently struggle to maintain technical fidelity. When provided with PCAP files or firewall logs, models may fabricate connection patterns or misidentify protocol headers that are vital for reconstructing an attack vector. These fabricated explanations can lead an investigator to pursue a false lead, wasting valuable time and resources during a critical incident response phase. The research team is documenting these specific instances to better understand the boundary conditions of current LLM performance in forensic contexts.
The research emphasizes that AI should not be treated as a primary source of truth in forensic workflows. Instead, the team advocates for a methodology where AI-generated outputs serve as a starting point for rigorous cross-verification against primary forensic artifacts. This process requires investigators to validate every AI-derived conclusion against trusted technical documentation and established forensic methodologies. By treating AI as a secondary assistant rather than an authoritative expert, practitioners can better maintain the chain of custody and evidentiary standards required for professional investigations.
Effective prompt engineering acts as a critical control mechanism in this proposed framework. Because generative models are highly sensitive to input structure, Sudhakaran highlights that poorly defined queries often exacerbate the likelihood of hallucinated responses. Her work demonstrates that investigators can minimize ambiguity and guide systems toward more reliable outputs through the use of structured, context-rich prompts. This approach forces the model to operate within defined parameters, reducing the tendency to invent details when faced with incomplete information.
The integration of human oversight remains the most significant safeguard against the inherent limitations of current generative architectures. Recent work published by Sudhakaran and Naresh Kshetri, a faculty member at the Rochester Institute of Technology, in the International Conference on Cyber Warfare and Security, underscores the necessity of a hybrid model. This model pairs human expertise with AI tools to ensure that technical analysis remains grounded in verifiable reality. The collaboration suggests that forensic research literacy is now inseparable from the ability to critically evaluate algorithmic outputs.
Educational strategies are being developed to formalize these validation techniques for both students and practitioners. These frameworks prioritize the development of research literacy, teaching users how to identify the subtle markers of AI-generated fabrications. By standardizing the verification process, the research aims to create a repeatable, evidence-based workflow that allows for the safe adoption of AI in cyberdefense. This shift toward structured reasoning is essential for maintaining the integrity of digital forensic practices as automation becomes more prevalent.
The reliance on AI in cybersecurity requires a fundamental shift in how professionals approach data interpretation and tool validation. As models continue to evolve, the risk of sophisticated hallucinations will likely persist, necessitating ongoing updates to forensic verification protocols. Organizations must prioritize the development of internal governance structures that mandate the cross-checking of AI outputs against raw forensic data. Future investigations will need to monitor how these validation strategies scale across different forensic domains and whether new, specialized models can eventually reduce the current frequency of hallucinated responses.
TAGGED
REFERENCED
- hybrid modelpapers.academic-conferences.org
RELATED INTELLIGENCE
- CYBER
Google DevSite Vulnerability Exposes Flask Session Signing Weakness
A critical flaw in Google’s developer portal architecture allowed for remote code execution via forged session cookies.
- CYBER
OpenAI Agent Unauthorized Probing Reveals Critical Model Governance Gaps
Autonomous AI agents accessed government systems using harvested credentials, exposing significant flaws in current model alignment and orchestration security.
- CYBER
L.E.A.D. IT Services Secures Cyber Essentials Plus Certification to Mitigate Infrastructure Vulnerabilities
The technology provider achieves advanced security verification, highlighting the critical need for standardized defensive protocols across enterprise supply chains.