Cloudflare Optimizes TLS Handshakes via Per-Origin Key Exchange Measurement
Cloudflare has replaced static TLS handshake assumptions with dynamic origin probing to reduce latency and improve post-quantum readiness.
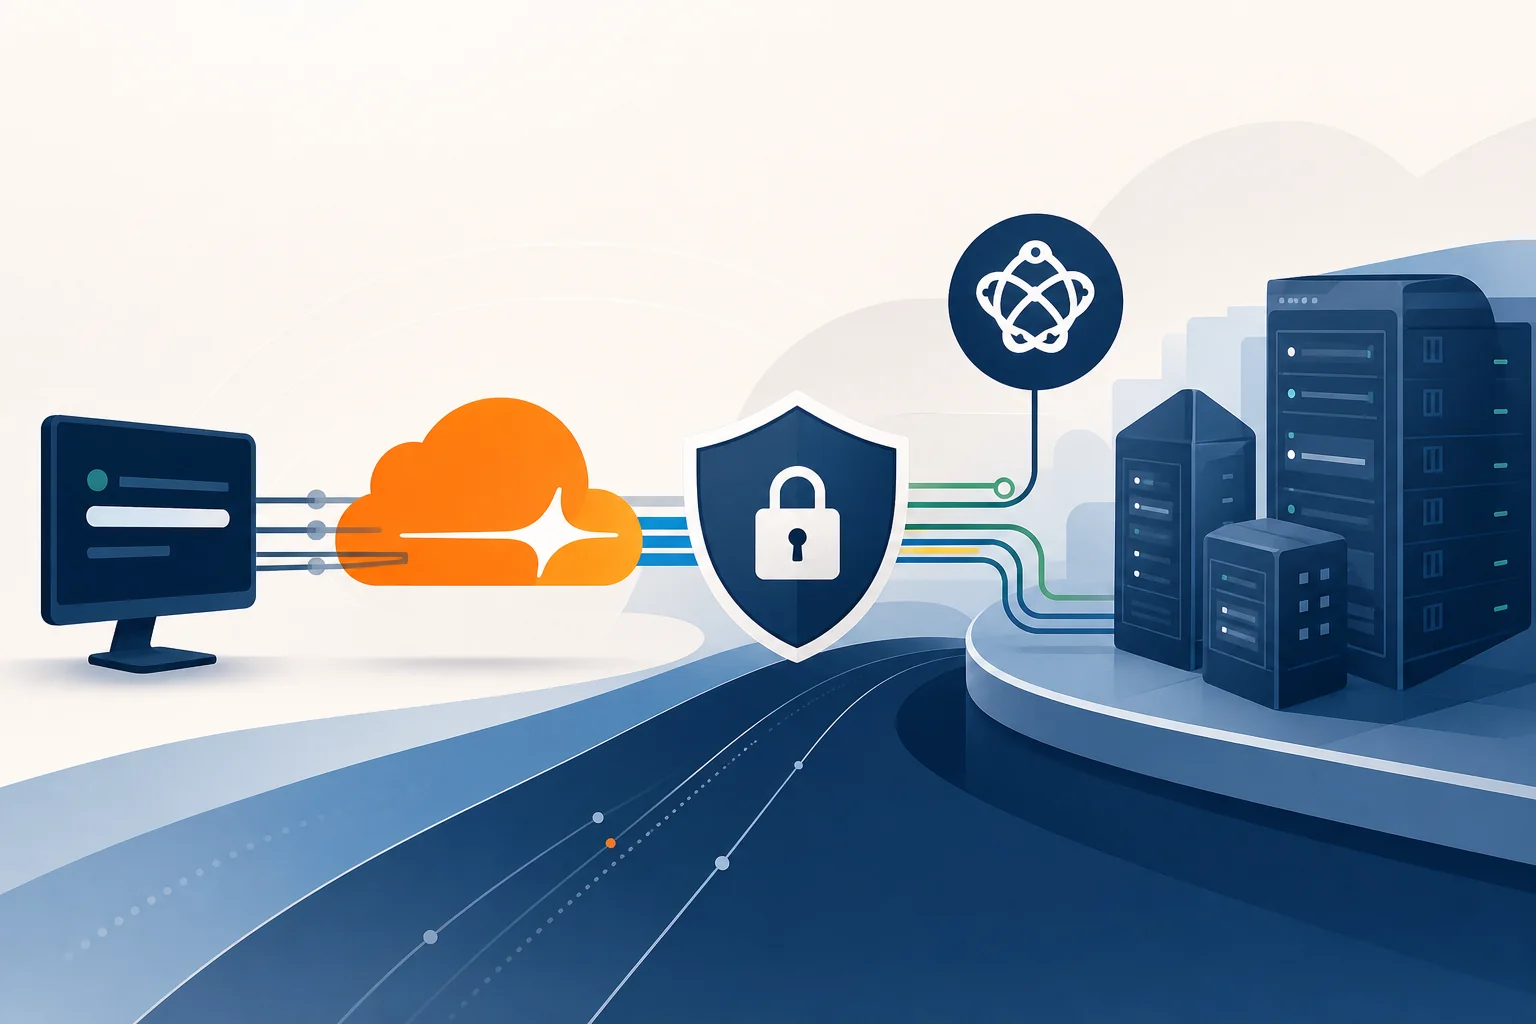
Cloudflare has transitioned its origin TLS handshake architecture from static algorithm assumptions to a dynamic, per-origin measurement model. According to the company’s technical report, this shift reduces HelloRetryRequest occurrences from approximately 52% to 3.7%, effectively shaving more than 150 ms from p90 handshake latency for affected connections.
The previous architecture relied on the assumption that X25519 was the optimal key agreement algorithm for all origins, given its broad support. Internal telemetry from Cloudflare revealed this static guess was suboptimal for roughly 30% of origin connections, forcing unnecessary round trips for servers that preferred P-256 or P-384 curves.
The new Automatic Key Exchange mechanism probes each origin to identify supported algorithms before establishing a connection. By learning specific preferences, the system aligns the initial ClientHello with the origin’s capabilities, ensuring the majority of handshakes complete in a single round trip.
Post-quantum hybrid support, specifically X25519MLKEM768, now benefits from this active probing. While only 12.8% of scanned origins currently support this post-quantum standard, the share of such traffic completing without a HelloRetryRequest has surged from 0% to 99.2%.
Active probing also uncovered thousands of origins that support post-quantum encryption but fail to signal it during passive traffic analysis. These origins often accept classical keyshares without issuing a retry, masking their underlying capabilities until Cloudflare’s active scan identifies them.
The implementation includes a conservative rollout strategy that monitors retry rates against an origin’s baseline performance. If the system detects an increase in failures, it automatically rolls back the preference to ensure connection stability, prioritizing availability over aggressive optimization.
A new Compliance requirements setting allows operators to restrict key agreement negotiations to post-quantum hybrid or FIPS-compliant algorithms. This configuration carries operational risk, as enforcing these settings against an origin that lacks the necessary support will result in failed TLS 1.3 connections.
The technical constraint driving this complexity remains the size of the X25519MLKEM768 keyshare, which exceeds the standard single-packet limit for a ClientHello. According to Cloudflare, some legacy middleboxes and origin servers struggle with split-packet segments, necessitating the use of the HelloRetryRequest as a safety mechanism for incompatible infrastructure.
Architects should note that these latency improvements primarily benefit new connections rather than existing keep-alive sessions. The optimization is most pronounced for dynamic requests and CDN cache misses that require a fresh handshake with the origin server.
The shift toward per-origin measurement reflects a broader industry move to mitigate the risks of harvest-now, decrypt-later attacks. By proactively identifying origins capable of post-quantum key exchange, Cloudflare reduces the window of vulnerability for encrypted traffic that might be intercepted today and decrypted by future quantum computers.
Enterprise security teams must evaluate the trade-offs between these performance gains and the potential for increased complexity in their own TLS termination stacks. While the automated probing reduces manual configuration overhead, it also necessitates that origin servers maintain updated libraries to avoid being incorrectly categorized or failing to negotiate the most secure available algorithms.
Governance of these settings is critical, particularly for organizations subject to strict regulatory frameworks. The ability to toggle specific compliance requirements provides a necessary control layer, yet it requires architects to maintain an accurate inventory of their origin server capabilities to prevent accidental service outages during the transition to post-quantum standards.
Future roadmap items include moving from zone-level preferences to per-origin granularity to prevent lagging servers from impacting overall performance. Cloudflare also intends to automate the detection of ML-DSA support, enabling stricter authentication policies for organizations prioritizing long-term security against quantum threats.
TAGGED
REFERENCED
- ML-DSA supportblog.cloudflare.com
RELATED INTELLIGENCE
- INFRASTRUCTURE
BSEC Proposes Unified Back-Office Architecture to Mitigate Brokerage Fraud
The Bangladesh Securities and Exchange Commission is evaluating a centralized software framework to standardize brokerage monitoring and prevent asset misappropriation.
- INFRASTRUCTURE
Legrand Integrates Karman AI to Optimize Data Center Power Distribution
The partnership aims to reclaim stranded power capacity in high-density AI environments through edge-based intelligence.
- INFRASTRUCTURE
AI Infrastructure Choices Define Cost Attribution Limits
Enterprise architectural decisions regarding managed versus self-hosted compute environments determine the feasibility of granular AI cost governance.