Eliminating Long-Lived Credentials in GCP via Workload Identity Federation
Shifting from static service account keys to federated trust relationships reduces credential exposure and operational overhead in enterprise cloud environments.
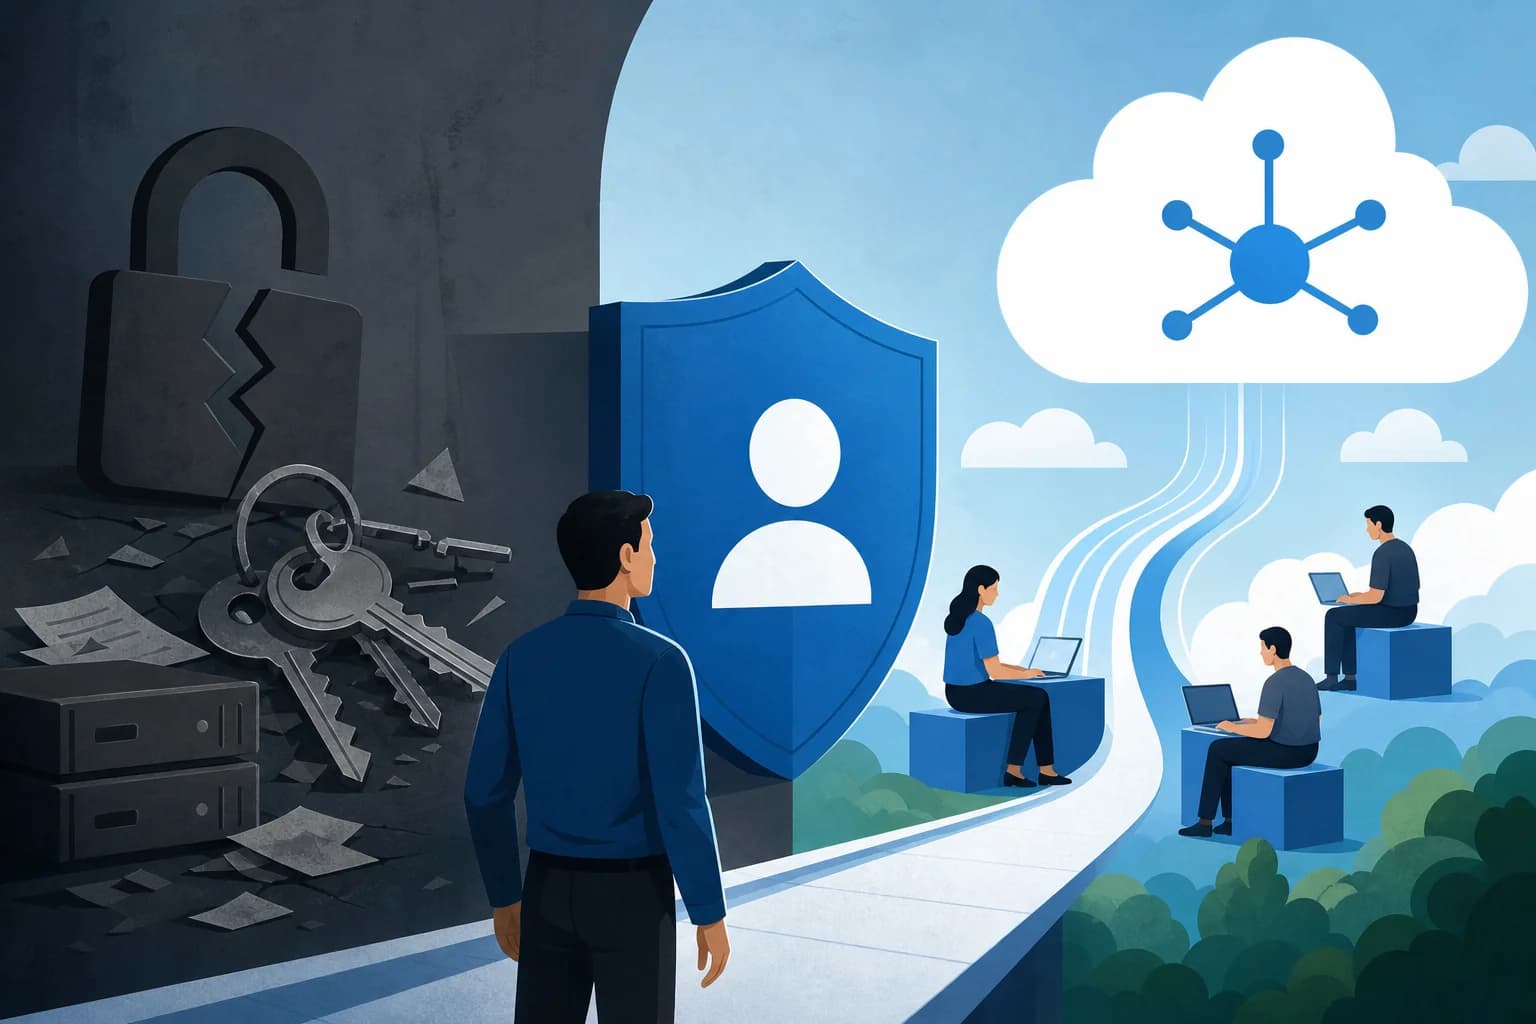
Organizations managing large-scale Google Cloud Platform (GCP) environments are increasingly moving away from static service account keys to mitigate the risks associated with long-lived credentials. Shijin Nair, an enterprise architect, details a strategy for implementing Workload Identity Federation (WIF) to replace traditional JSON keys that often persist indefinitely in CI/CD pipelines and third-party integrations.
The primary architectural shift involves moving from a model of secret management to one of configured trust relationships. Instead of distributing sensitive credentials that require manual rotation, WIF allows external workloads to authenticate using native tokens validated by GCP’s Security Token Service. This process eliminates the need for storing secrets in environment variables or version control systems, effectively reducing the blast radius of potential credential leaks.
Implementation of WIF relies on a three-part structure consisting of a workload identity pool, an OIDC provider, and specific service account bindings. A workload identity pool serves as a container for trust configurations, while the provider acts as the connector that validates incoming tokens from external platforms. The final binding grants the authenticated workload temporary, scoped access to GCP resources, ensuring that permissions are strictly tied to the identity of the requesting process.
Attribute conditions function as the critical security gate within this framework, preventing overly broad access by verifying specific claims within the incoming token. Without these conditions, any identity from a trusted provider could potentially authenticate, which poses significant risks in production environments. By utilizing Common Expression Language (CEL) syntax, architects can define granular rules that restrict access to specific repositories, pipelines, or service accounts.
Adopting WIF at scale requires a strategic approach to legacy infrastructure, as retrofitting existing keys can introduce significant operational risk. Rather than attempting a full migration of every active key, organizations can mandate WIF for all new project provisioning to halt the proliferation of static credentials. This policy effectively treats legacy keys as a fixed, shrinking problem set rather than an immediate, high-risk migration project.
The operational benefits of this mandate extend beyond security, as it enforces standardized scoping conventions across all development teams. Because every new project inherits the same federated pattern, architectural consistency is maintained from the outset. This approach prevents the divergence of security designs and simplifies the integration of new CI/CD tools, such as Harness or GitHub Actions, by leveraging existing, trusted configurations.
Technical leaders must recognize that WIF is not a proprietary GCP concept but an implementation of standard identity protocols. Similar mechanisms, such as Microsoft Entra Workload ID, utilize OIDC-based federated credentials to achieve the same goal of eliminating stored secrets. The underlying model of exchanging an external token for a short-lived platform token provides a consistent security posture across multi-cloud and hybrid environments.
The transition to federated identity requires careful monitoring of the OIDC connector configuration, specifically the issuer URL and attribute mappings. GCP fetches public keys from the issuer URL to verify the authenticity of incoming tokens, making the integrity of this endpoint a primary security concern. Proper mapping of external claims to GCP attributes is essential to ensure that the correct permissions are granted to the authorized workload.
Architects should evaluate the trade-offs between direct access and impersonation when configuring service account bindings. While direct access is the default, impersonation often provides a more robust mechanism for managing granular permissions in complex, multi-org setups. Monitoring the audit logs remains a necessary practice, even with WIF, to ensure that the trust relationships are functioning as intended and that no unauthorized identities are attempting to leverage the federation.
Future infrastructure planning should prioritize the total elimination of long-lived keys as a standard governance requirement. As organizations continue to scale their cloud footprint, the operational overhead of manual key rotation will become increasingly unsustainable. Establishing a clear roadmap for the deprecation of legacy keys while enforcing WIF for all new deployments will be a decisive factor in maintaining a secure and manageable cloud architecture.
TAGGED
REFERENCED
- Security Token Servicedocs.cloud.google.com
- Common Expression Language (CEL)github.com
- Microsoft Entra Workload IDlearn.microsoft.com
RELATED INTELLIGENCE
- CLOUD
AWS Rebuilds EventBridge Architecture with Enhanced Custom Event Buses
The new EventBridge architecture addresses long-standing technical debt by introducing native cross-account routing and refined subscriber management.
- CLOUD
Oracle Analyst Sentiment Diverges Amid Cloud Infrastructure Expansion
Recent shifts in brokerage price targets reflect complex market reactions to Oracle’s evolving enterprise cloud and database strategy.
- CLOUD
Modernizing Enterprise Case Management Through Unified Data Architecture
Senior architect Rajarshi Krishna Muppaneni details the shift toward integrated digital ecosystems to eliminate operational silos and improve regulatory compliance.